Offensive Security
Understanding how systems are attacked — and how to defend them.
Red TeamPentestingActive DirectoryReconnaissanceOSINTPost-Exploitation
Cybersecurity Student·Offensive Security·Red Team
I build security tools and research projects to understand how systems work, how they can be attacked, and how they can be secured.
I started programming at around 10 years old, initially learning C# and Unity through game development. Over time, my curiosity shifted from creating games to understanding the systems underneath them — and that curiosity led me to cybersecurity and offensive security.
Today, I am studying Systems and Microcomputer Networks (SMR) and focusing my learning on Red Team, penetration testing, Active Directory, Windows/Linux, OSINT, malware research and AI-assisted cybersecurity.
I learn primarily by building. Instead of only using existing security tools, I create my own projects to understand the technologies and the problems behind them. My projects range from Red Team orchestration and C2 infrastructure to distributed systems, malware research and AI-driven security tooling.
My goal is to start my professional career in cybersecurity and eventually specialize in Red Team operations and offensive security research.
Not a list of percentages — areas I actively work in, backed by the projects below.
Understanding how systems are attacked — and how to defend them.
Building the tooling an operator actually needs.
Using AI as a force multiplier — never as a blind autopilot.
The foundations everything else stands on.
Four engineering projects — each one built to answer a real question about offensive security. Real screenshots, real usage, no mock-ups.
 Active researchFeaturedHover to preview
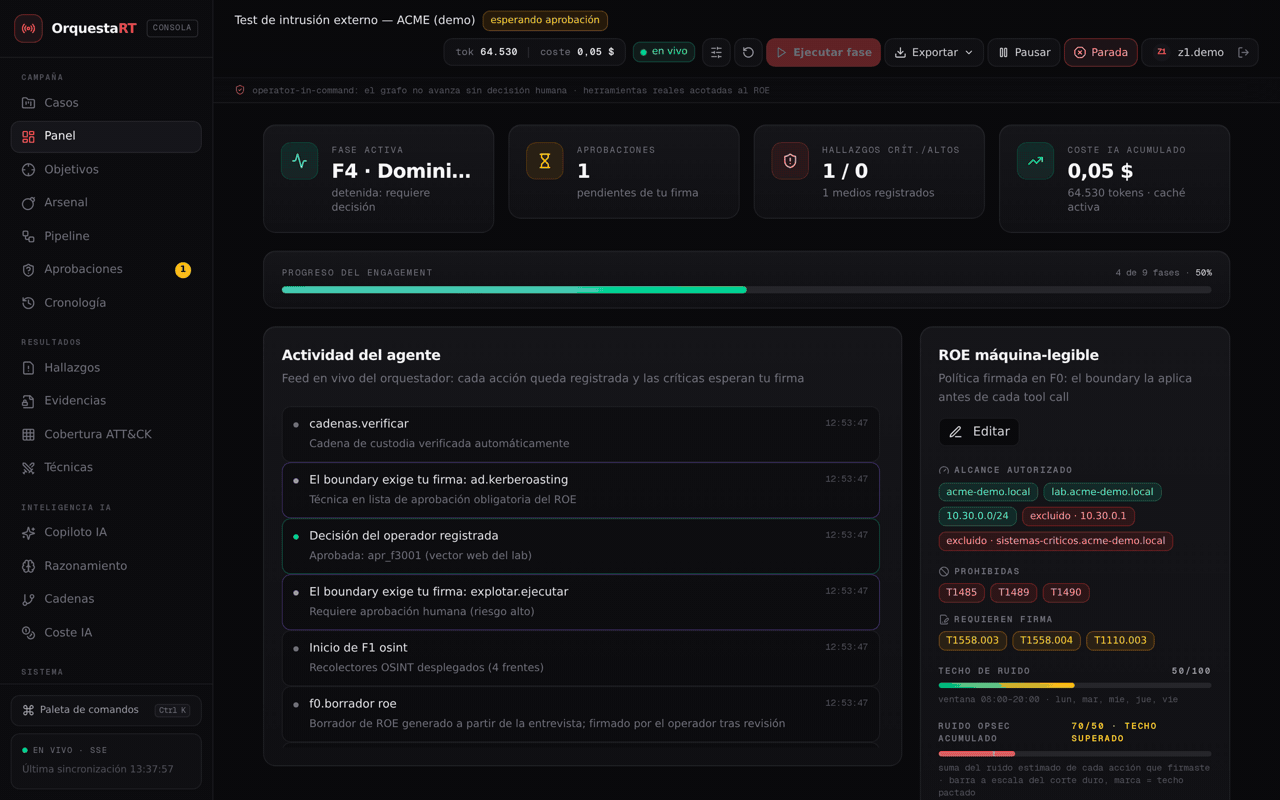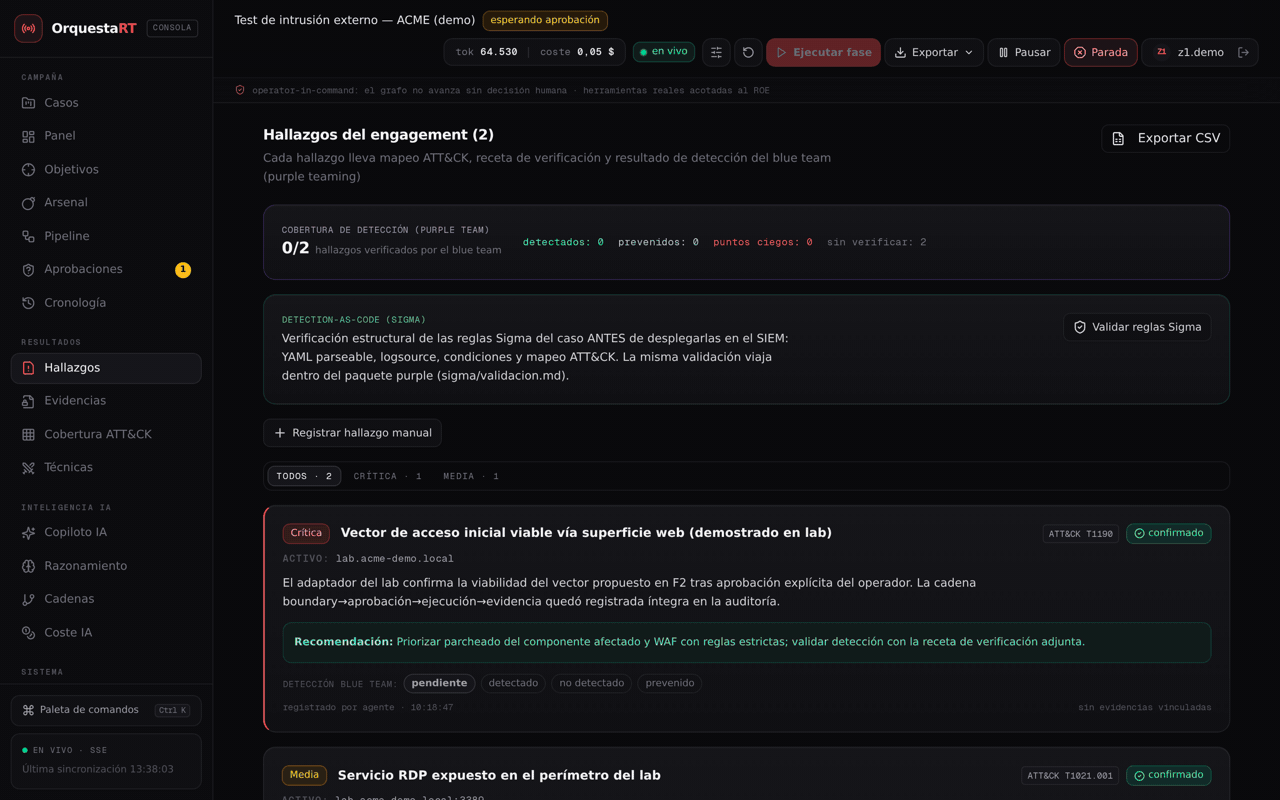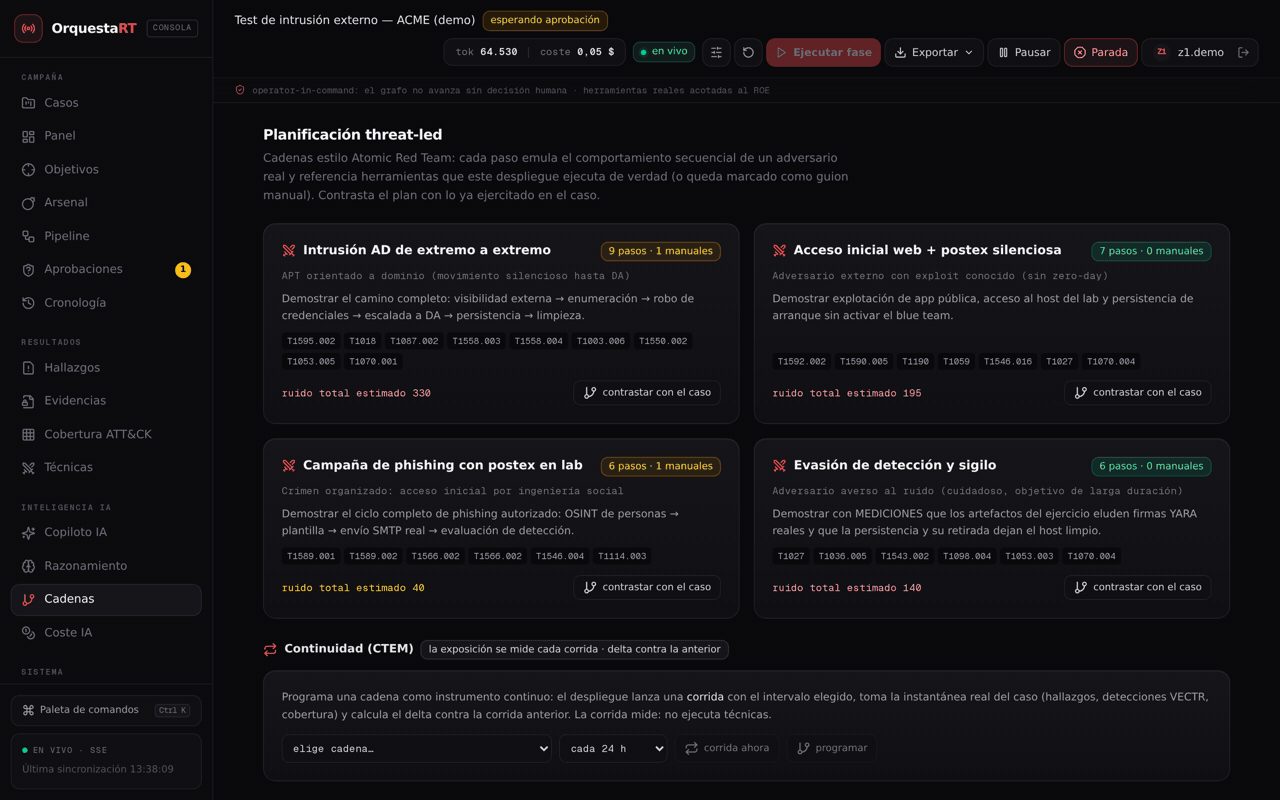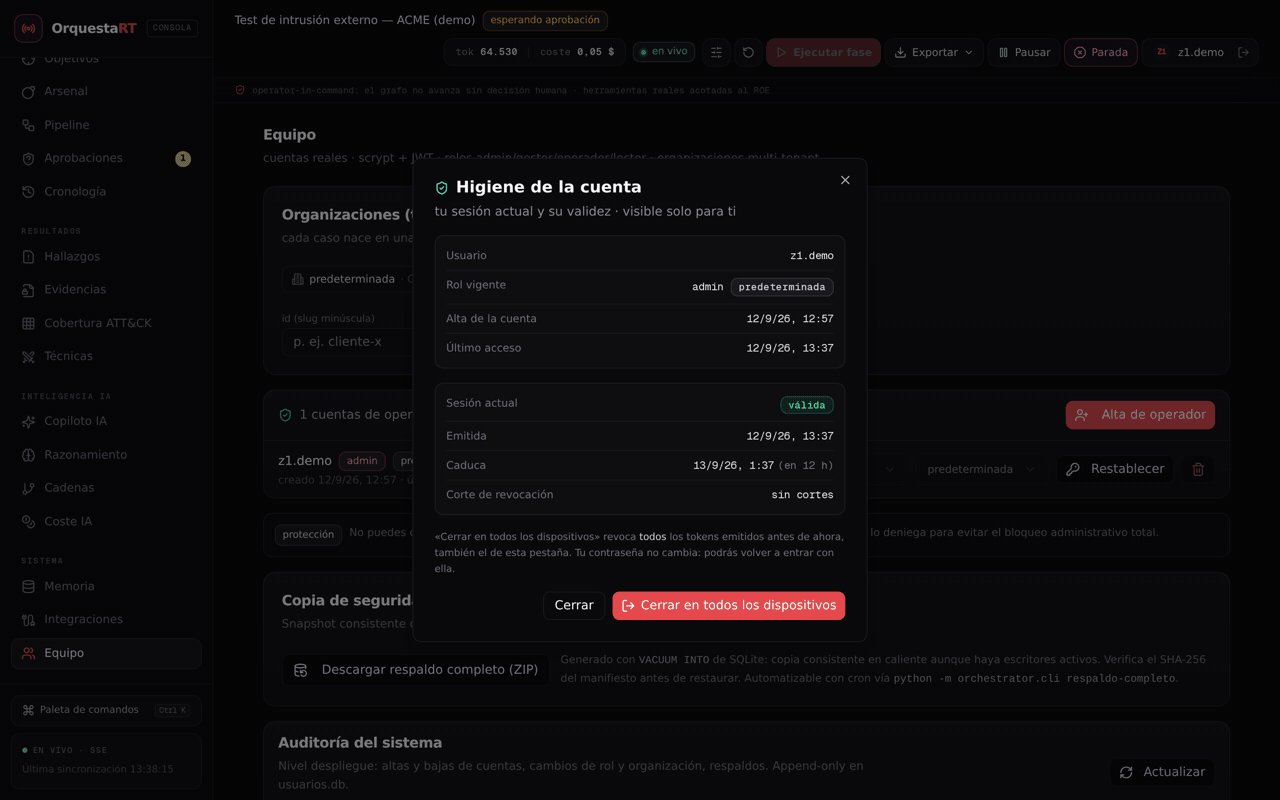
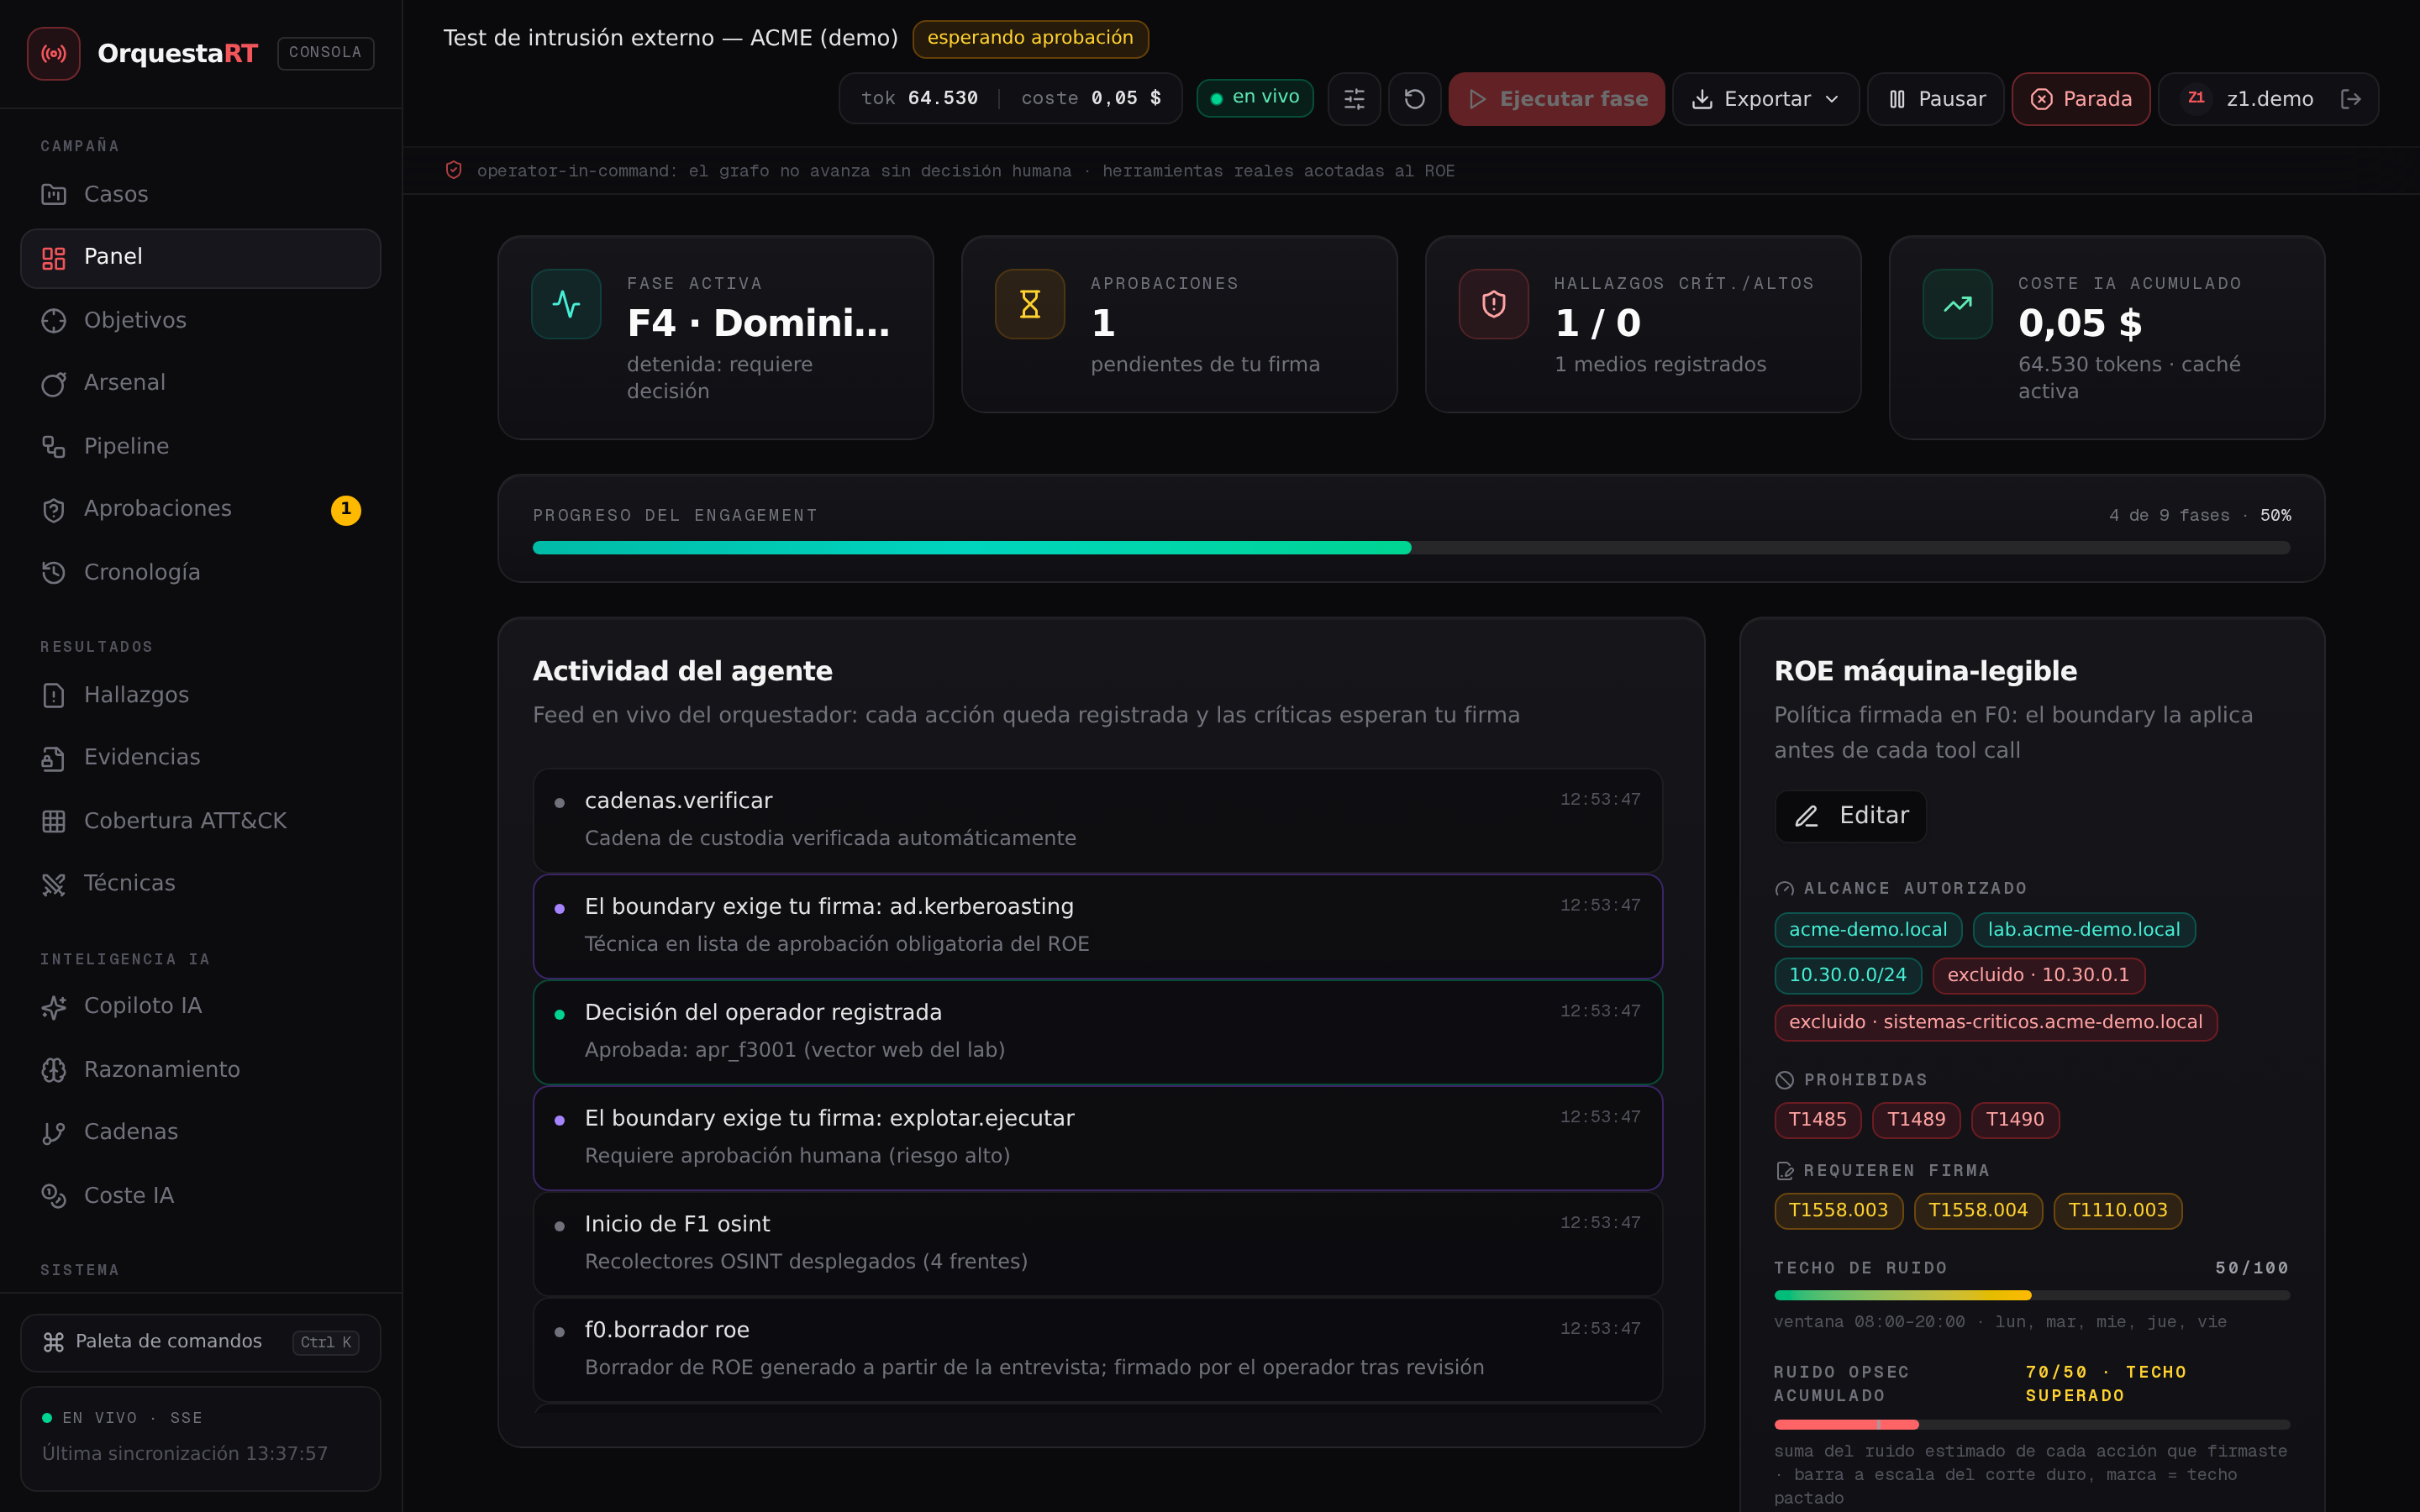
AI-assisted Red Team Orchestration Platform
A platform for orchestrating authorized Red Team operations through AI-assisted workflows — combining offensive security automation with human approval, scope enforcement and full auditability.
The full engagement cycle — scoping, OSINT, recon, Active Directory, post-exploitation, phishing, reporting — orchestrated by agents under a machine-readable ROE, with purple teaming as a first-class output.
 Active researchHover to preview
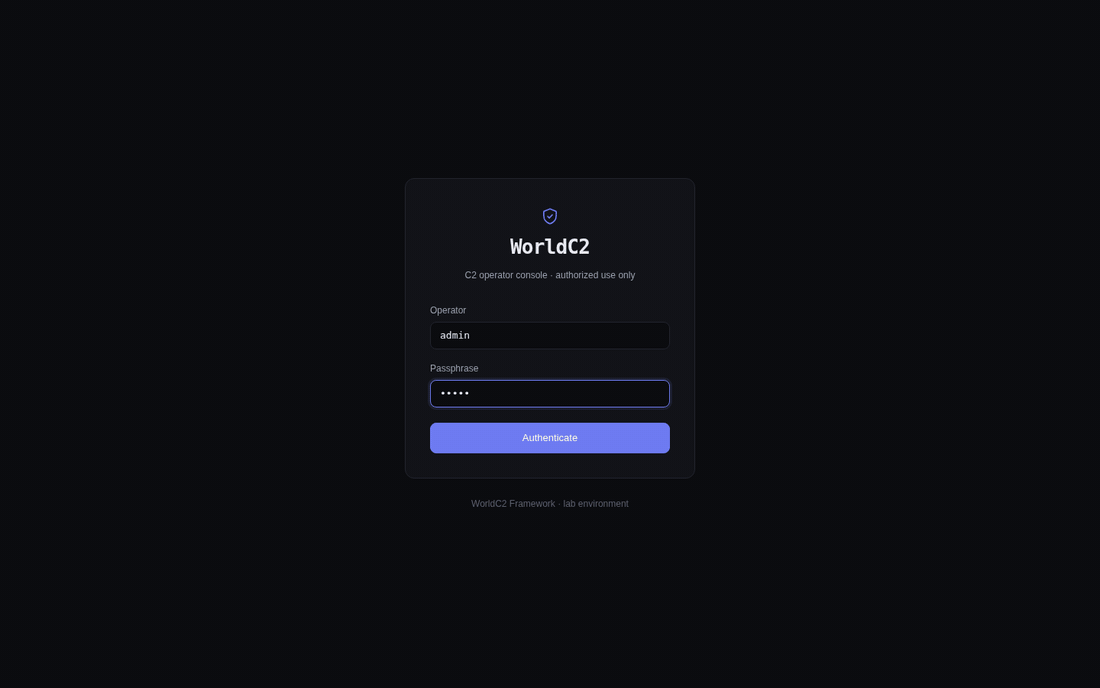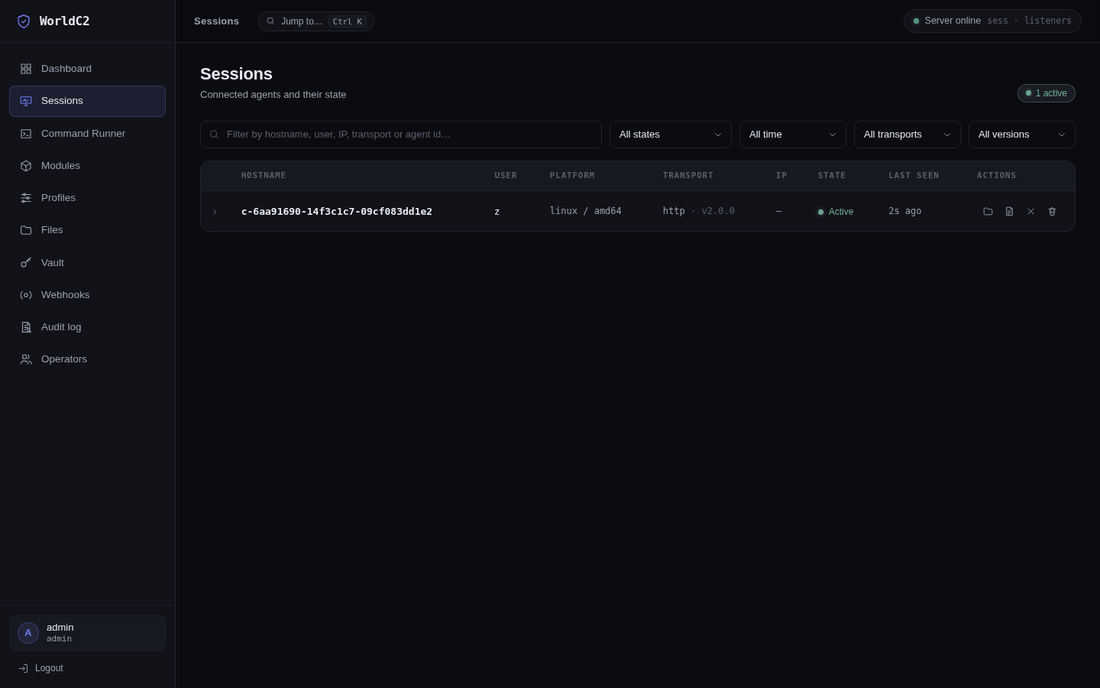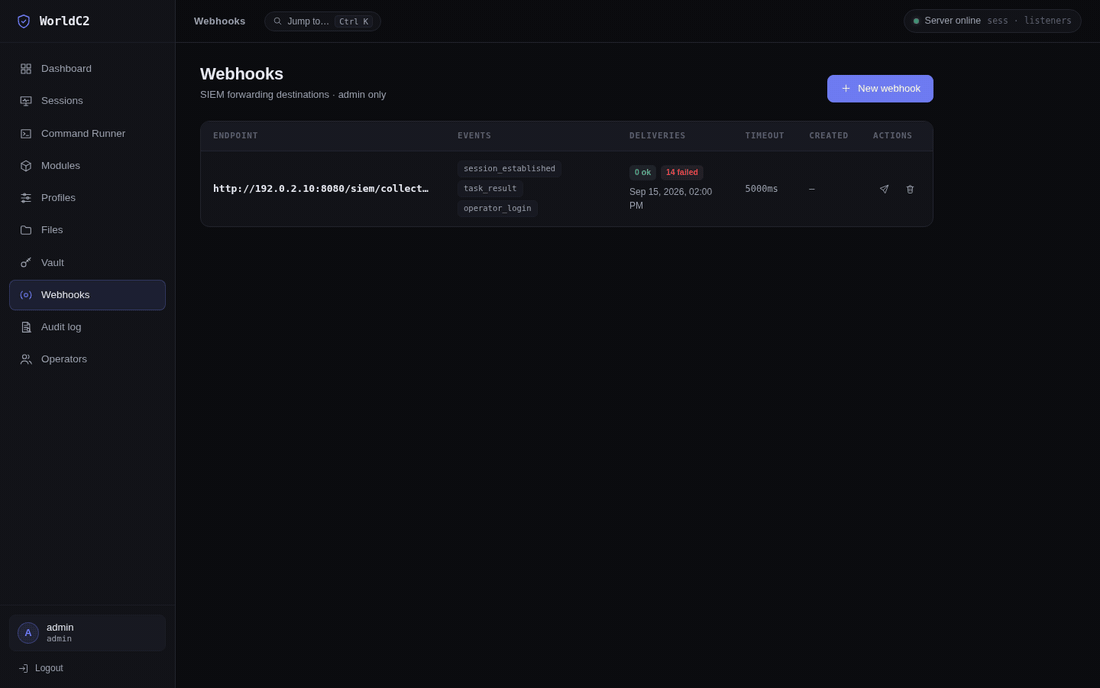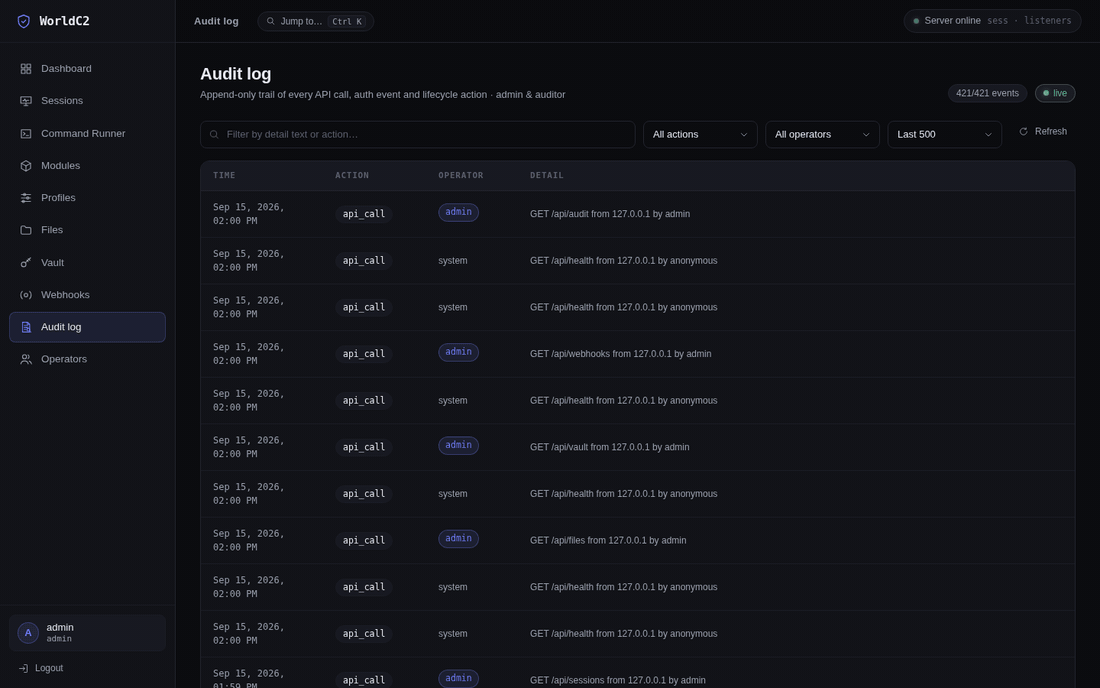
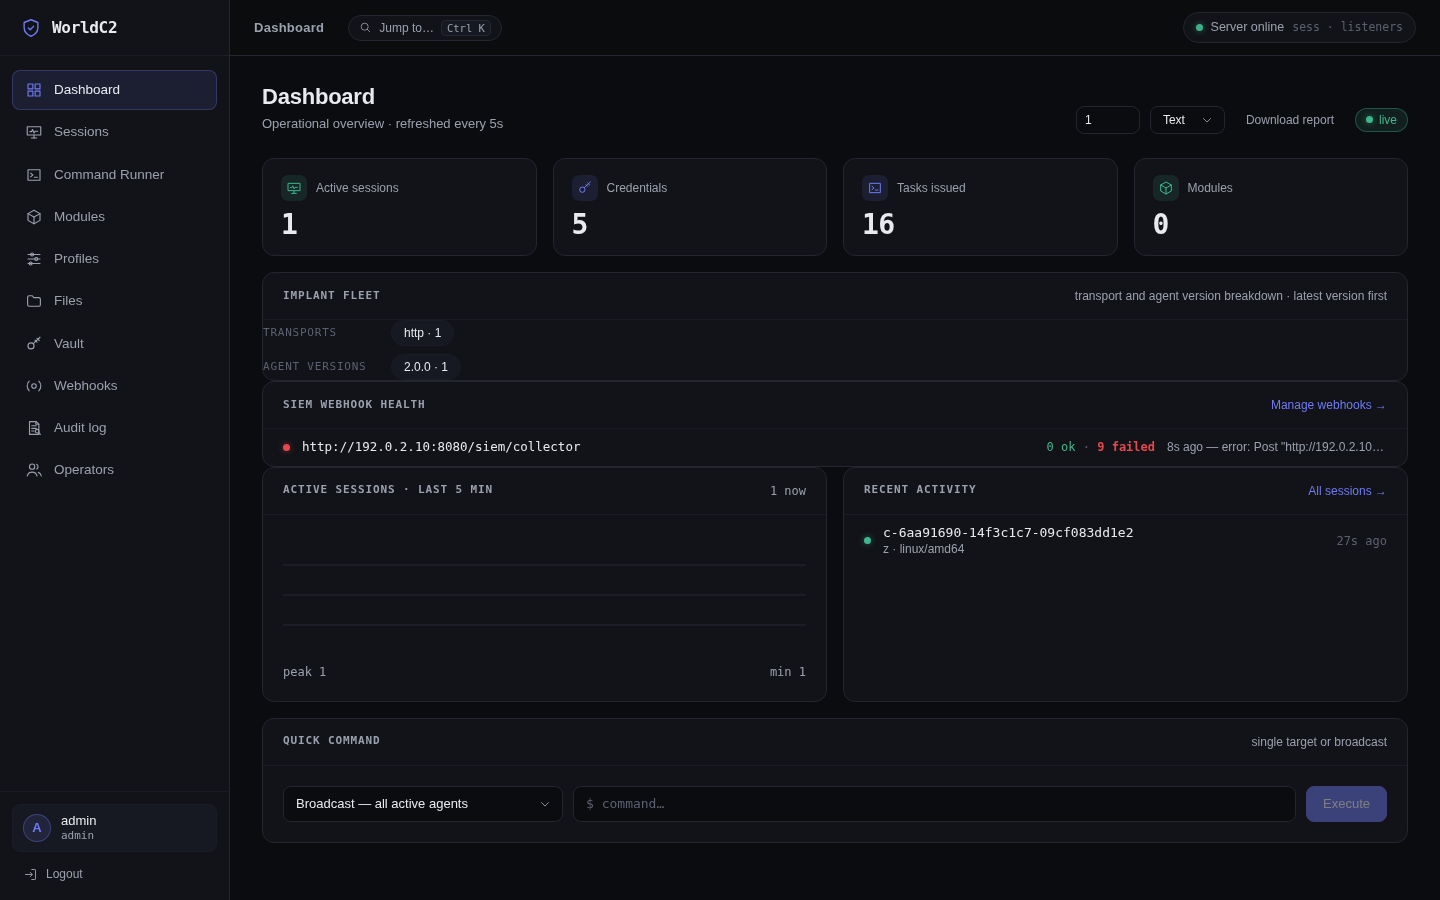
Command & Control Platform for Authorized Security Labs
A C2 platform developed as a security research and learning project — focused on understanding command-and-control architecture, encrypted communications, session management and operator infrastructure.
Built to understand how modern C2 infrastructure is designed, secured and operated in controlled environments.
 Active researchHover to preview
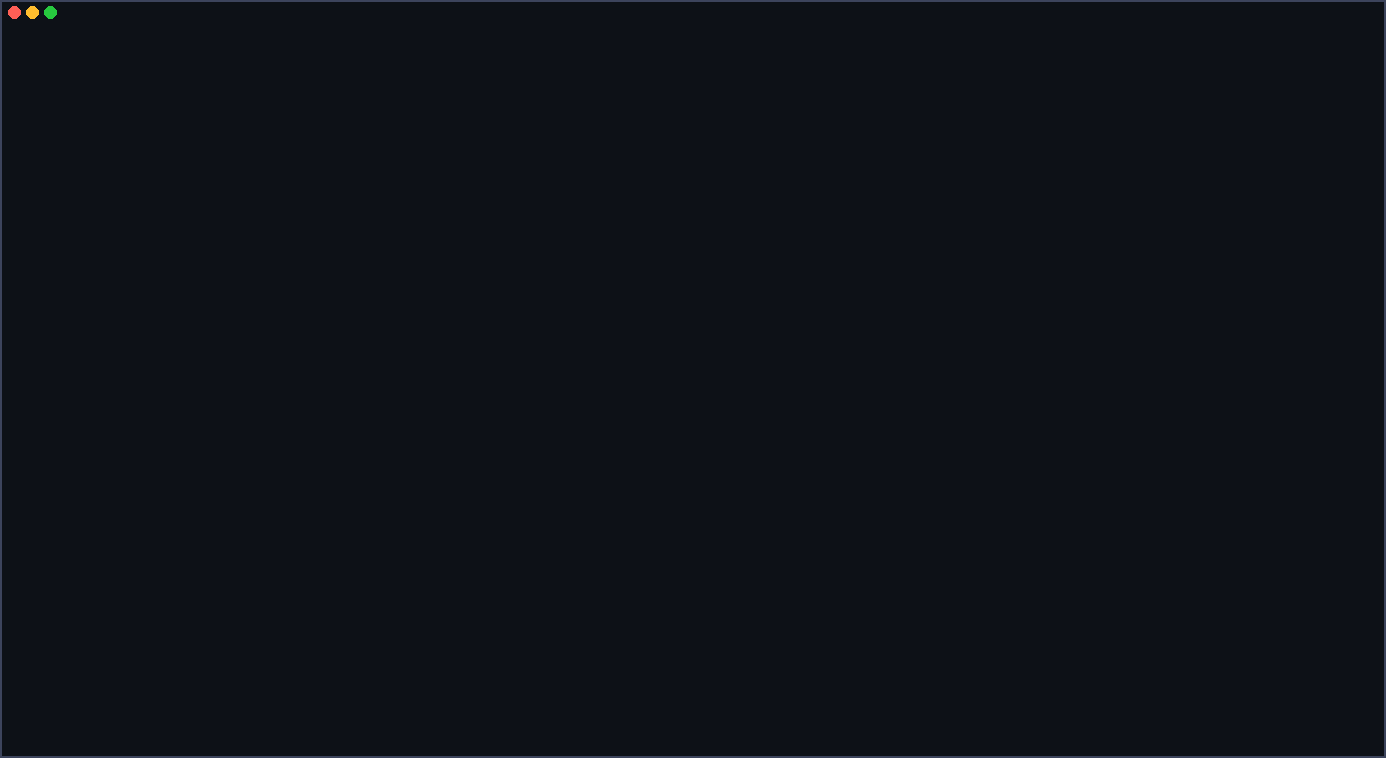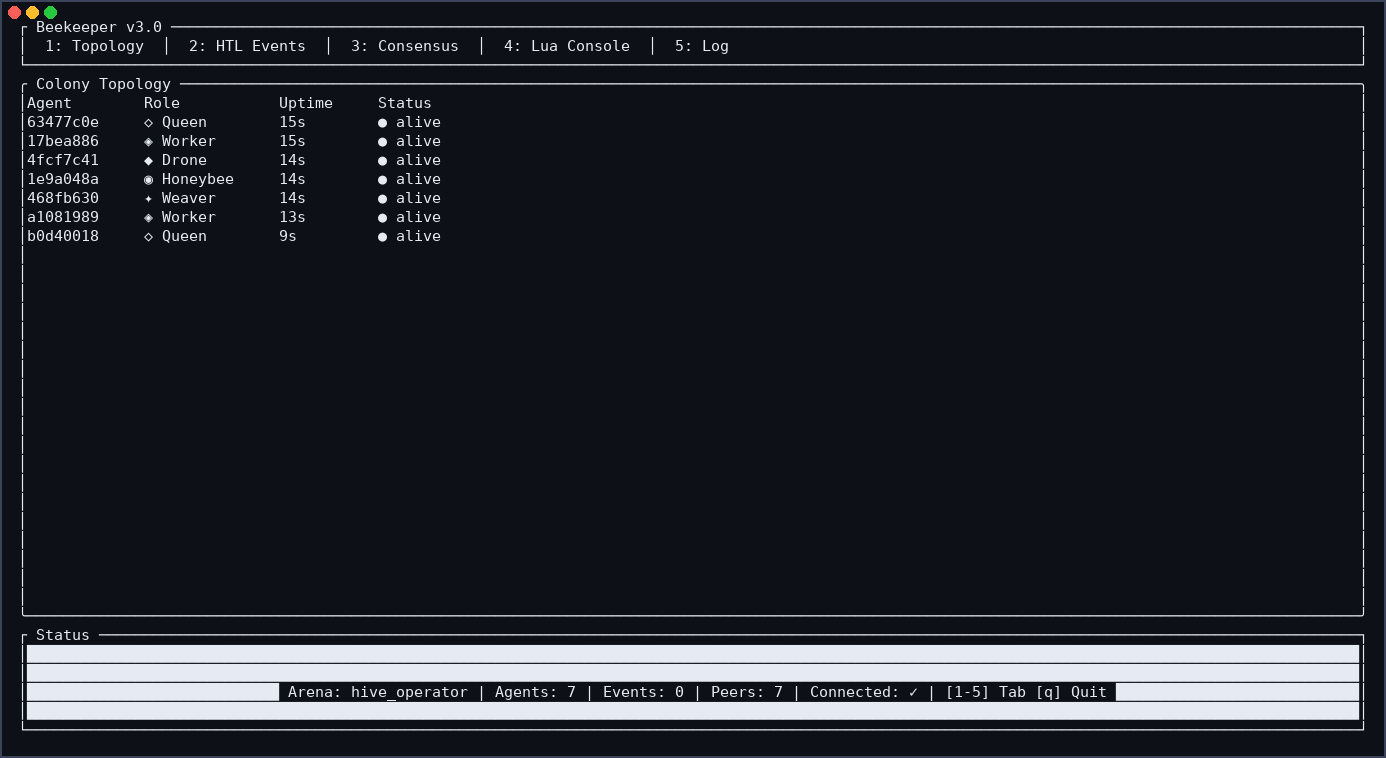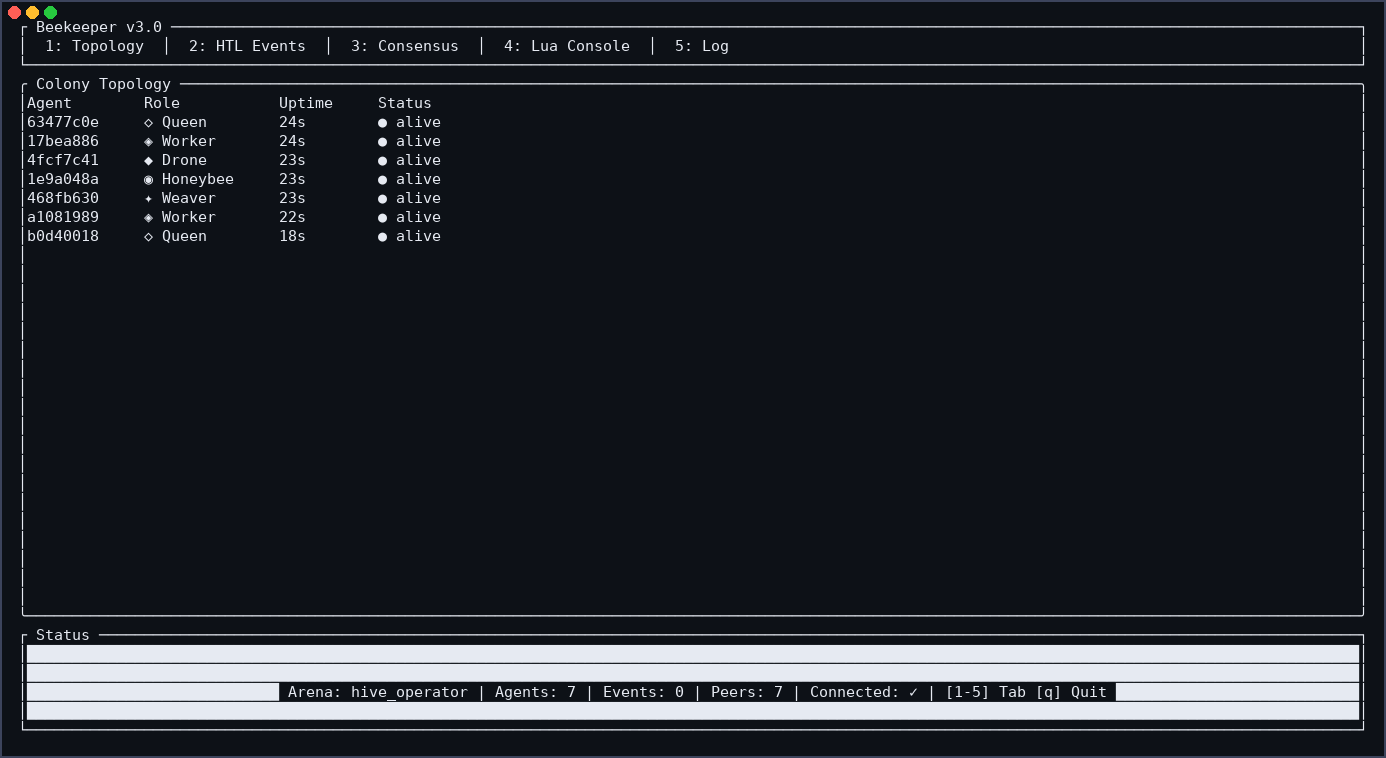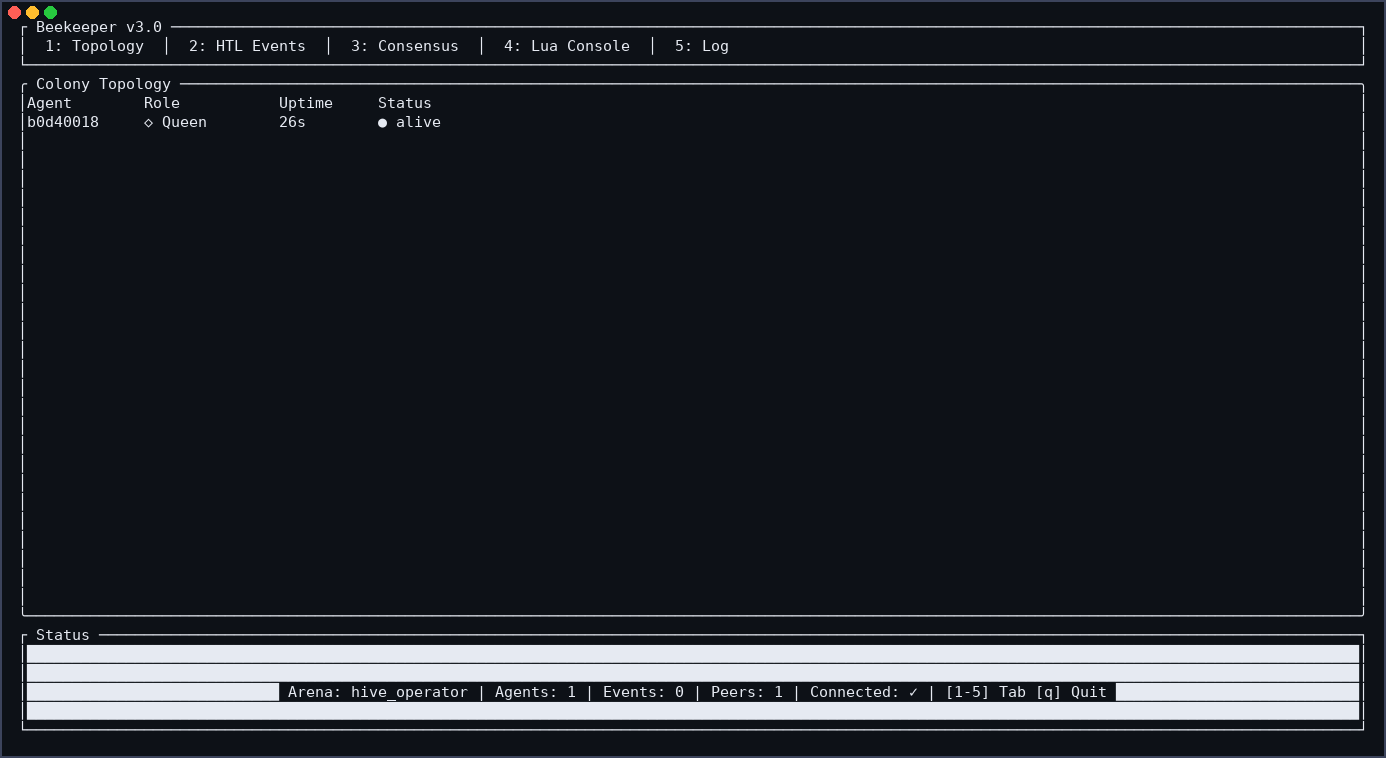
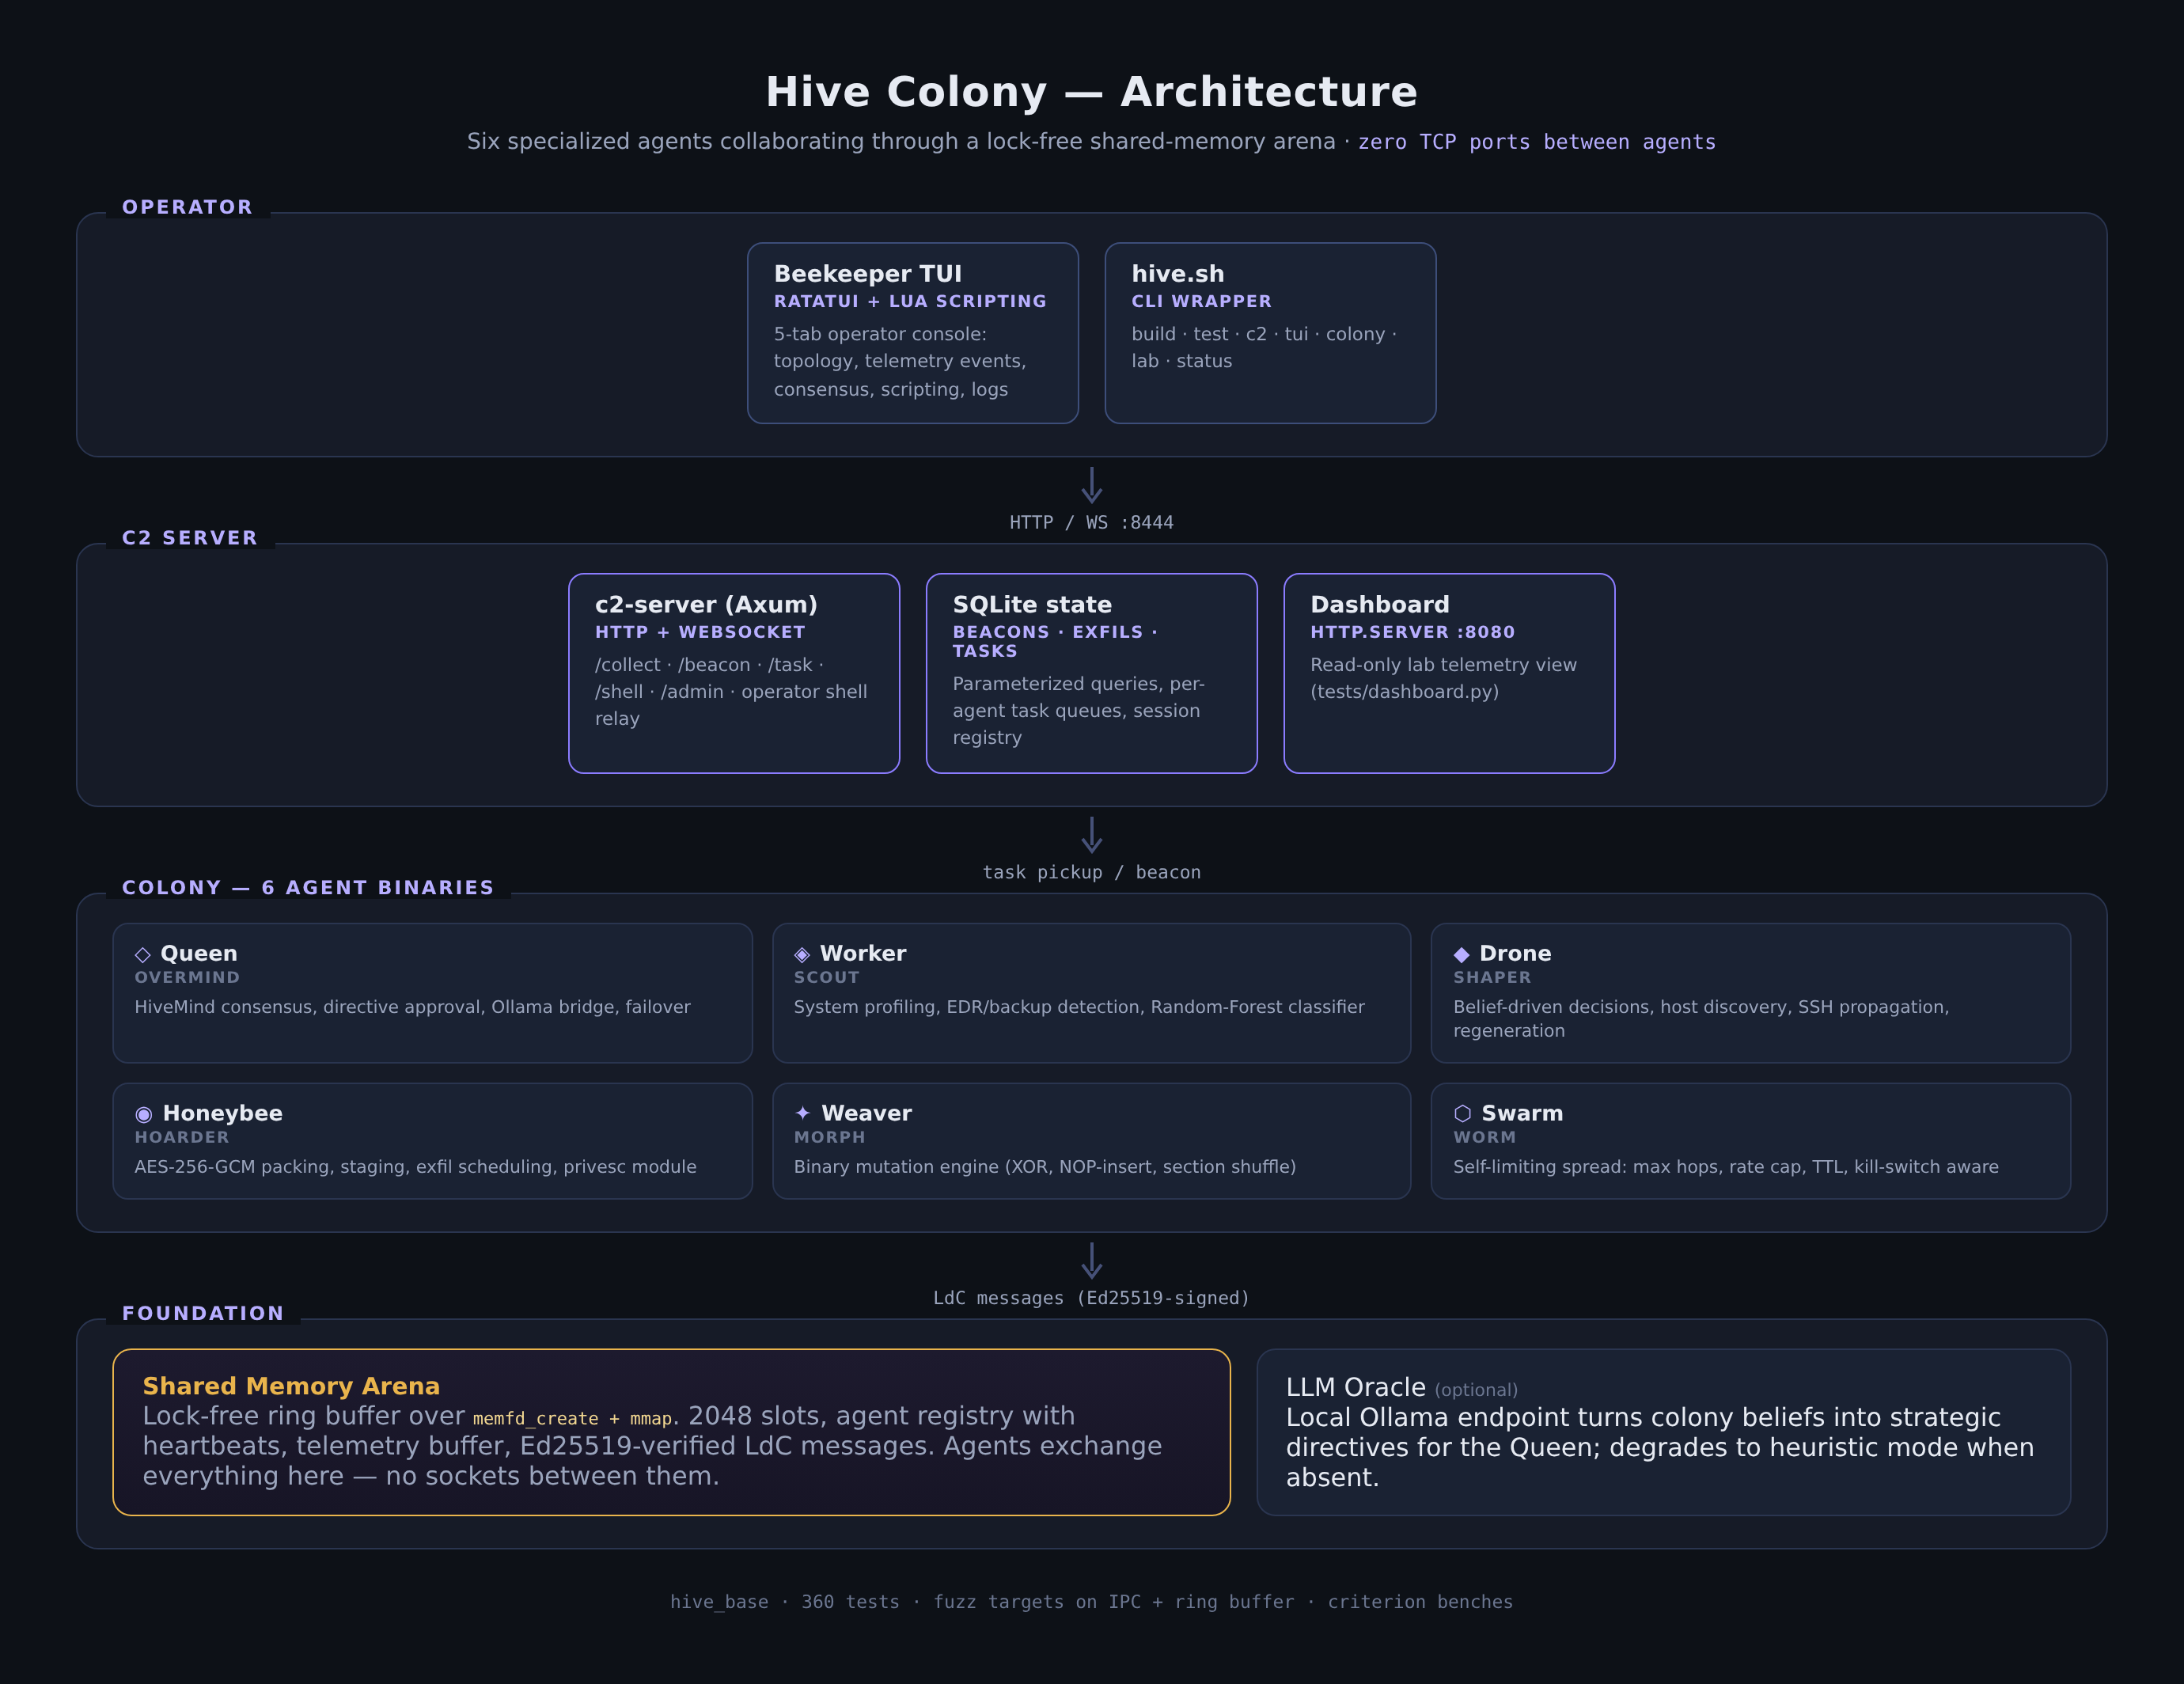
Distributed Multi-Agent Security Research
A Rust-based experimental project exploring multi-agent coordination, distributed systems, concurrency, consensus and AI-assisted security research.
One of my most technically challenging projects — built to learn Rust and to explore how autonomous agents can coordinate under shared rules.
 Research completeHover to preview
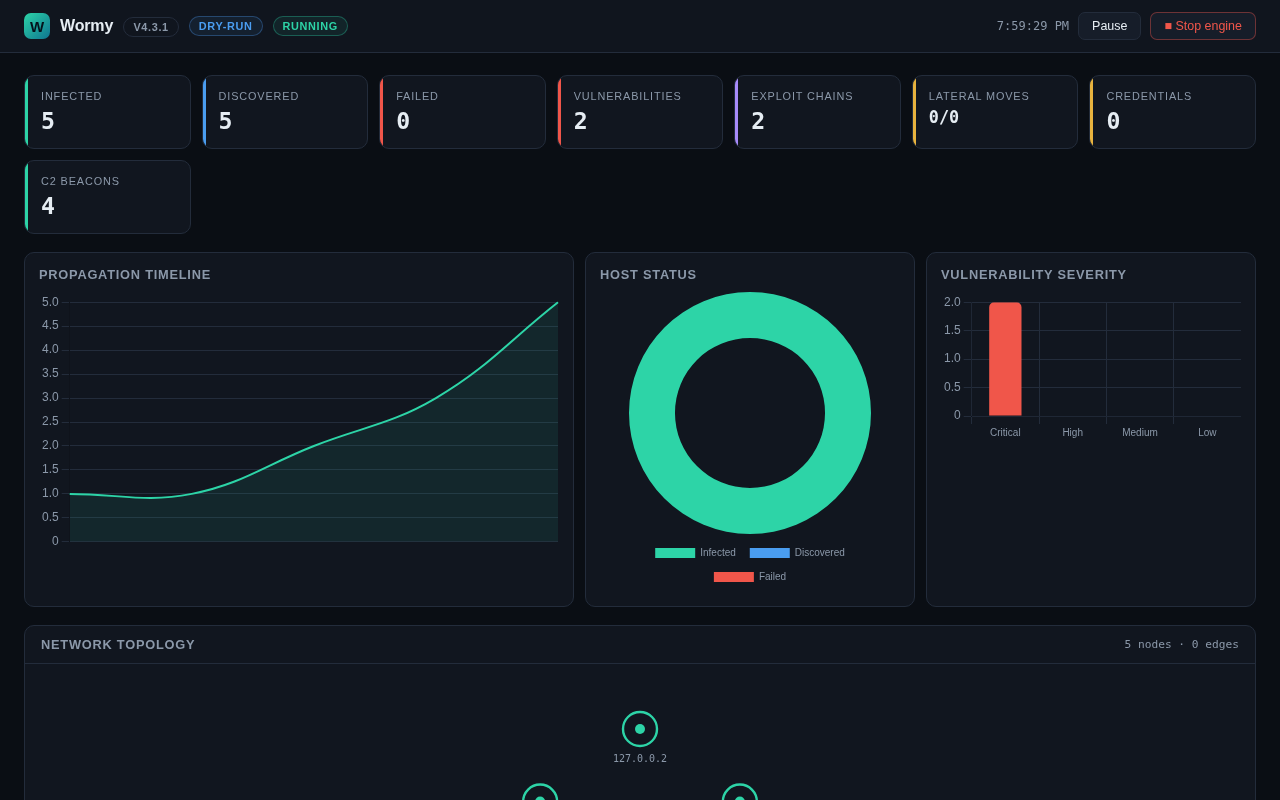
Malware & Network Security Research
An experimental research project exploring malware behavior, network propagation and machine learning in isolated laboratory environments.
My first major malware research project — and one of the projects that shaped my interest in understanding offensive techniques from the inside.
“I learn by building.”
When I want to understand a technology or a security concept, I try to implement it myself. Building these projects forces me to understand the systems underneath the tools I use, to experiment with different approaches and to learn from failures.
I also use AI as a development and research assistant, but I treat generated code as something to review, test and understand — not something to blindly trust.
My goal is not just to make something work, but to understand why it works.
Only tools and technologies I have actually used in real projects.
Foundation level
INE Security
Previously certified · Expired July 2026
Cisco Networking Academy
Relevant coursework completed
Hack4u
Red Team & pentesting coursework
Next professional milestones
Red Team Operator training path
Deepening adversary emulation and Red Team tradecraft.
Penetration Testing training path
Structured preparation for professional penetration testing certifications.
No logos shown as if already earned — only what is real.
Theory is nothing without hands-on practice.
Building experience through practical labs and realistic attack scenarios — active machines, AD paths and CTF-style challenges.
Self-built isolated environments: Active Directory domains, deliberately vulnerable services, C2 infrastructure and detection tooling — where every project on this page runs.
Validating offensive work against detection: Sigma rule authoring, VECTR-style tracking and ATT&CK coverage measurement.
Evidence that goes beyond code.
Team Captain · 1st place Málaga · Spain National Final
Captain of a robotics team that finished first in Málaga and qualified for the national final in Spain.
Worked on robot development, problem-solving, team coordination and competition strategy — under real time pressure and against the best teams in the country.
// leadership · teamwork · competition strategy — skills that don't show up in a git log
DigitechFP
Systems administration, computer networks, operating systems and cybersecurity fundamentals — the formal backbone of my self-taught path.
EVAD
My entry door to programming: C#, Unity and the discipline of shipping playable software. The curiosity about how things worked under the hood started here.
Deepening practical offensive security skills: methodology, tradecraft and hands-on labs.
Preparing for CRTO and CPTES as the next professional milestones.
Improving Windows and enterprise environment attack methodology — from enumeration to domain dominance.
Building experience through practical labs and realistic attack scenarios.
Continuing to build and refine offensive security research projects.